Experiencing a security incident? Get emergency responseCall now +91 90083 72466 Quick inquiry

VAPT Security Services

Vulnerability Assessment and Penetration Testing Services Company

Find security weaknesses before attackers do. We at CipherTrivia, a leading VAPT company in Bangalore, combine automated vulnerability assessment with expert-led penetration testing to identify security gaps, validate real-world risks and provide clear remediation guidance. From web applications and APIs to networks and infrastructure, our VAPT security services help businesses understand what is vulnerable, what can actually be exploited and what needs to be fixed first.

Reporting mapped to OWASP Top 10 OWASP API Top 10 CWE CVSS ISO 27001 SOC 2 PCI DSS

What Is VAPT

Vulnerability Assessment and Penetration Testing Services for Your Digital Infrastructure

Vulnerability Assessment and Penetration Testing (VAPT) is a cybersecurity testing process used to discover security vulnerabilities and determine how attackers could exploit them. A Vulnerability Assessment identifies and classifies potential weaknesses across applications and infrastructure, while Penetration Testing uses controlled attack techniques to validate the exploitability and impact of those vulnerabilities. VAPT is commonly performed for web applications, mobile applications, APIs, networks, servers, cloud environments and other internet-facing or business-critical systems.

At CipherTrivia, a trusted VAPT testing company, we perform VAPT by first defining the testing scope and understanding the target environment. Our security team then conducts automated vulnerability scanning followed by manual security testing and controlled penetration testing to validate significant findings. We assess authentication, authorization, access controls, APIs, application logic, configurations and other relevant attack surfaces based on the agreed scope. AI-assisted security analysis supports vulnerability discovery and technical analysis while our security professionals validate the findings before they are reported.

We offer VAPT service for various industries and sectors including businesses, enterprises, SaaS companies, startups, government organizations and technology teams that need to identify security risks in their digital systems. It is particularly valuable before launching a new application, after major application or infrastructure changes, during periodic security assessments and when organizations need security evidence for customer or compliance requirements. Our VAPT security testing produces findings with severity ratings, technical evidence and remediation recommendations, with optional retesting to verify that reported vulnerabilities have been addressed.
Scope of Work

What Is Included in Our VAPT Services?

At CipherTrivia, we provide Vulnerability Assessment and Penetration Testing (VAPT) services to identify, validate and prioritize security vulnerabilities across web applications, mobile applications, APIs, networks and cloud environments. We combine automated vulnerability scanning with manual penetration testing to uncover exploitable security weaknesses and provide technical remediation guidance. Our VAPT security testing services follow industry-recognized practices with a strong focus on application security, infrastructure security and risk-based vulnerability assessment.

12 Workstreams

Our VAPT Security Testing Services Include:

Web Application VAPT

We perform comprehensive web application penetration testing to identify vulnerabilities such as SQL injection, Cross-Site Scripting (XSS), broken access control, authentication flaws, session vulnerabilities, insecure configurations and other OWASP security risks.

Mobile Application VAPT

We assess Android and iOS applications for security weaknesses involving insecure data storage, weak authentication, improper session handling, API vulnerabilities, reverse engineering risks and insecure communication.

API Security Testing

We conduct API penetration testing to identify broken authentication, authorization issues, excessive data exposure, injection attacks, insecure endpoints and other vulnerabilities that can compromise API security.

Network VAPT

Our network vulnerability assessment and penetration testing covers servers, network devices, exposed ports, services and configurations to identify vulnerabilities that could provide unauthorized access to your infrastructure.

Infrastructure Security Testing

We assess IT infrastructure for outdated software, exposed services, security misconfigurations and known vulnerabilities that could increase the attack surface of your organization.

Authentication & Authorization Testing

We test login mechanisms, password policies, session management, privilege escalation and role-based access controls to identify vulnerabilities that could allow unauthorized users to access restricted resources.

OWASP Vulnerability Testing

We test applications against common OWASP Top 10 vulnerabilities and related application security risks. Our testing focuses on identifying practical vulnerabilities that could affect confidentiality, integrity and availability.

Manual Penetration Testing

We go beyond automated vulnerability scanning with manual security testing and penetration testing. Our security testers validate vulnerabilities and assess their potential impact through controlled attack scenarios.

Vulnerability Risk Assessment

We classify identified vulnerabilities based on severity and business impact. Critical and high-risk vulnerabilities receive priority so your technical team can focus on the security issues that require immediate attention.

VAPT Security Report

We provide a detailed VAPT assessment report covering vulnerability descriptions, affected assets, severity ratings, technical evidence, potential impact and recommended remediation actions.

Remediation Support

We provide technical guidance to help development and infrastructure teams understand the root cause of identified vulnerabilities and implement appropriate security fixes.

VAPT Retesting

After remediation, we perform VAPT retesting on applicable findings to verify that vulnerabilities have been fixed and that the implemented changes have reduced the identified security risk.

Methodology

How Our VAPT Security Services Process Works

At CipherTrivia, our VAPT security services follow a structured security testing process that combines vulnerability assessment with manual penetration testing. We first understand your application or infrastructure scope and then identify security weaknesses through automated scanning and manual testing. Our security team validates exploitable vulnerabilities before documenting the findings with severity ratings and remediation recommendations. After fixes are implemented, we can perform VAPT retesting to verify the effectiveness of the remediation.

  1. Scope & Security Assessment Planning

    We define the testing scope, target applications, APIs, mobile platforms, IP addresses and infrastructure components. This helps us establish the VAPT testing methodology and assessment boundaries before security testing begins.

  2. Vulnerability Assessment

    We conduct automated and manual vulnerability assessment testing to identify known vulnerabilities, insecure configurations, outdated components and potential attack vectors across the approved scope.

  3. Manual Penetration Testing

    We manually validate identified vulnerabilities and perform controlled attack simulations to determine their actual security impact. This helps us identify vulnerabilities that automated scanners may not detect.

  4. Vulnerability Analysis & Risk Classification

    We analyze every validated finding and classify vulnerabilities based on severity and potential business impact. Critical and high-risk vulnerabilities receive higher remediation priority.

  5. Detailed VAPT Report

    We prepare a comprehensive VAPT security report with technical findings, affected assets, vulnerability severity, evidence and recommended remediation steps. The report gives your technical team a clear view of the security risks identified during testing.

  6. Remediation Support

    We work with your technical team by providing practical remediation guidance for identified security vulnerabilities. Our recommendations focus on addressing the root cause rather than only resolving the visible security issue.

  7. VAPT Retesting

    Once remediation is completed, we conduct VAPT retesting for applicable findings. We verify the implemented fixes and document the updated security status of the tested vulnerabilities.

Business Case

Why Businesses Need VAPT Security Testing

Businesses depend on web applications, mobile apps, APIs, cloud infrastructure and connected systems to manage critical operations and sensitive information. Vulnerability Assessment and Penetration Testing (VAPT) helps identify security weaknesses before attackers can exploit them. At CipherTrivia, we assess your technology environment through automated vulnerability discovery and manual security testing so your team can understand the actual risks affecting your applications and infrastructure.

Triggers

When Is VAPT Required?

Before Launching a New Application

We assess web applications, mobile apps and APIs before production deployment to identify vulnerabilities that could expose your users or business systems.

After Major Application Updates

New features, authentication changes, API integrations and business logic updates can introduce security weaknesses. We test the modified attack surface and validate significant findings.

After Infrastructure or Cloud Changes

Server migrations, cloud deployments and network configuration changes can introduce new exposure. Our infrastructure VAPT services help identify vulnerabilities within the updated environment.

Before Security Audits or Customer Assessments

We provide structured VAPT reports with technical evidence, severity ratings and remediation recommendations that can support internal security reviews and applicable customer or audit requirements.

When Handling Sensitive Data

Organizations processing financial information, personal data, healthcare information or confidential business records can use VAPT to identify vulnerabilities that may expose sensitive information.

After a Security Incident

We can assess affected systems to identify potential attack vectors and security weaknesses that may have contributed to an incident.

As Part of Periodic Security Testing

Applications and infrastructure continuously change as new features, integrations and dependencies are introduced. Regular VAPT security testing helps businesses identify newly introduced vulnerabilities and maintain better visibility into their security posture.

Audience

Who Should Consider VAPT?

SaaS companies, fintech businesses, healthcare organizations, ecommerce platforms, IT companies, startups and enterprises can benefit from professional VAPT services. At CipherTrivia, we define the testing scope according to your application architecture and infrastructure so our VAPT security assessment focuses on the systems and attack surfaces that matter most to your business.

Next step

Identify Security Risks Before Attackers Do

Strengthen your application and infrastructure with professional VAPT security testing from CipherTrivia. Our security team combines vulnerability assessment, manual penetration testing and AI-assisted analysis to identify exploitable weaknesses and provide clear remediation guidance.

Deliverables

What You Receive From Our VAPT Security Services

At CipherTrivia, we provide more than a vulnerability list. Our VAPT security assessment report gives your development, security and management teams the technical evidence they need to understand security risks, prioritize remediation and track vulnerability closure. We structure our Vulnerability Assessment and Penetration Testing services around clear findings with CVSS severity, evidence, remediation guidance and retesting support.

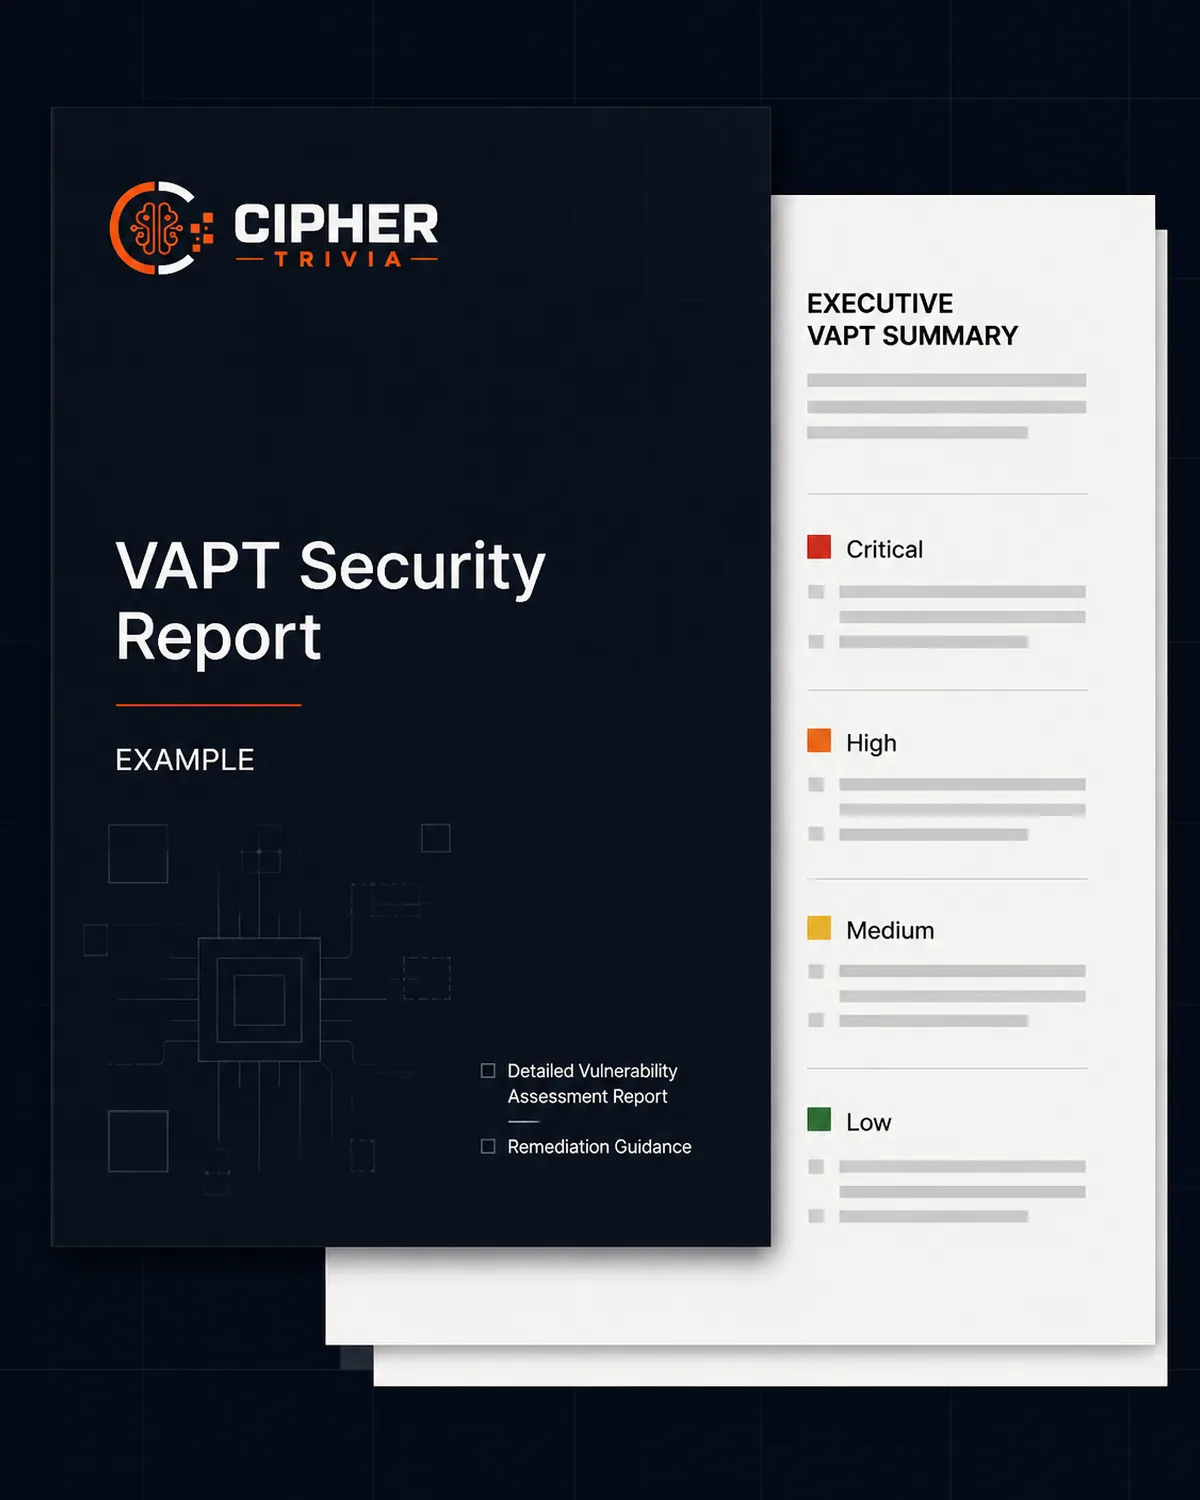
Example VAPT report with an executive summary and severity-rated findings
  1. Executive VAPT Summary

    We provide an executive-level overview of the security assessment findings with risk severity, key vulnerabilities and potential business impact. This section gives non-technical stakeholders a clear understanding of the overall security posture.

  2. Detailed Vulnerability Assessment Report

    We document every validated security vulnerability with its CVSS score, severity level, affected asset, technical description and proof-of-concept evidence. Our findings include sufficient technical detail to help security and development teams reproduce and investigate the issue.

  3. CipherTrivia Technical Remediation Guidance

    We provide practical remediation recommendations for each vulnerability. Our findings can be mapped to relevant OWASP and CWE references, helping developers understand the root cause and implement appropriate security fixes.

  4. CipherTrivia VAPT Findings Walkthrough

    We conduct a detailed walkthrough with your technical and management teams to explain the identified vulnerabilities, attack scenarios and potential impact. Our security testers answer technical questions and help prioritize the remediation roadmap.

  5. CipherTrivia VAPT Retesting & Closure Report

    After remediation, we perform VAPT retesting to validate the fixes for applicable findings. We document the retest results and provide a closure report that can support internal security reviews, customer assessments and compliance requirements.

  6. CipherTrivia AI-Assisted Security Insights

    Where applicable, we use AI-assisted analysis to help organize vulnerability data, identify patterns across findings and improve security reporting workflows. Human-led security validation remains central to our VAPT methodology so AI insights complement rather than replace penetration testing expertise.

Why CipherTrivia

Why Choose CipherTrivia for VAPT Security Services?

Our team at CipherTrivia, a trusted VAPT service provider, approaches Vulnerability Assessment and Penetration Testing (VAPT) as a technical security assessment rather than a basic automated scan. Our VAPT security services combine experienced security testing with AI-assisted analysis and manual validation so your team receives actionable findings with clear evidence, risk classification and practical remediation guidance.

Senior Security Testers

Our VAPT security testing is performed with experienced security professionals who manually validate identified vulnerabilities. We go beyond standard automated scans to assess attack paths and determine the actual impact of security weaknesses.

AI-Assisted Security Testing

We use AI-assisted security analysis to support vulnerability discovery, reconnaissance and technical analysis. Human security experts validate the findings before they are included in the final VAPT assessment report, keeping AI as a supporting layer within our testing methodology.

Validated Security Findings

We focus on actionable and technically validated vulnerabilities instead of filling reports with unverified scanner results. Each significant finding is reviewed for exploitability so your development and security teams can prioritize genuine risks.

Compliance-Focused VAPT Reporting

Our VAPT reports can be structured around relevant security and compliance requirements with mappings to frameworks such as OWASP, CWE and CVSS. This gives your technical and compliance teams useful documentation for security reviews and audit preparation.

Clear Remediation Guidance

We provide technical remediation recommendations alongside vulnerability findings. Your development team can use the report to understand the root cause, assess the security impact and plan the appropriate fix.

Transparent VAPT Process

From scope definition and vulnerability assessment to penetration testing, reporting and retesting, we maintain a structured process with clear deliverables. This gives stakeholders better visibility into the security assessment and the status of identified vulnerabilities.

Proof of Work

A VAPT Security Services Case Study

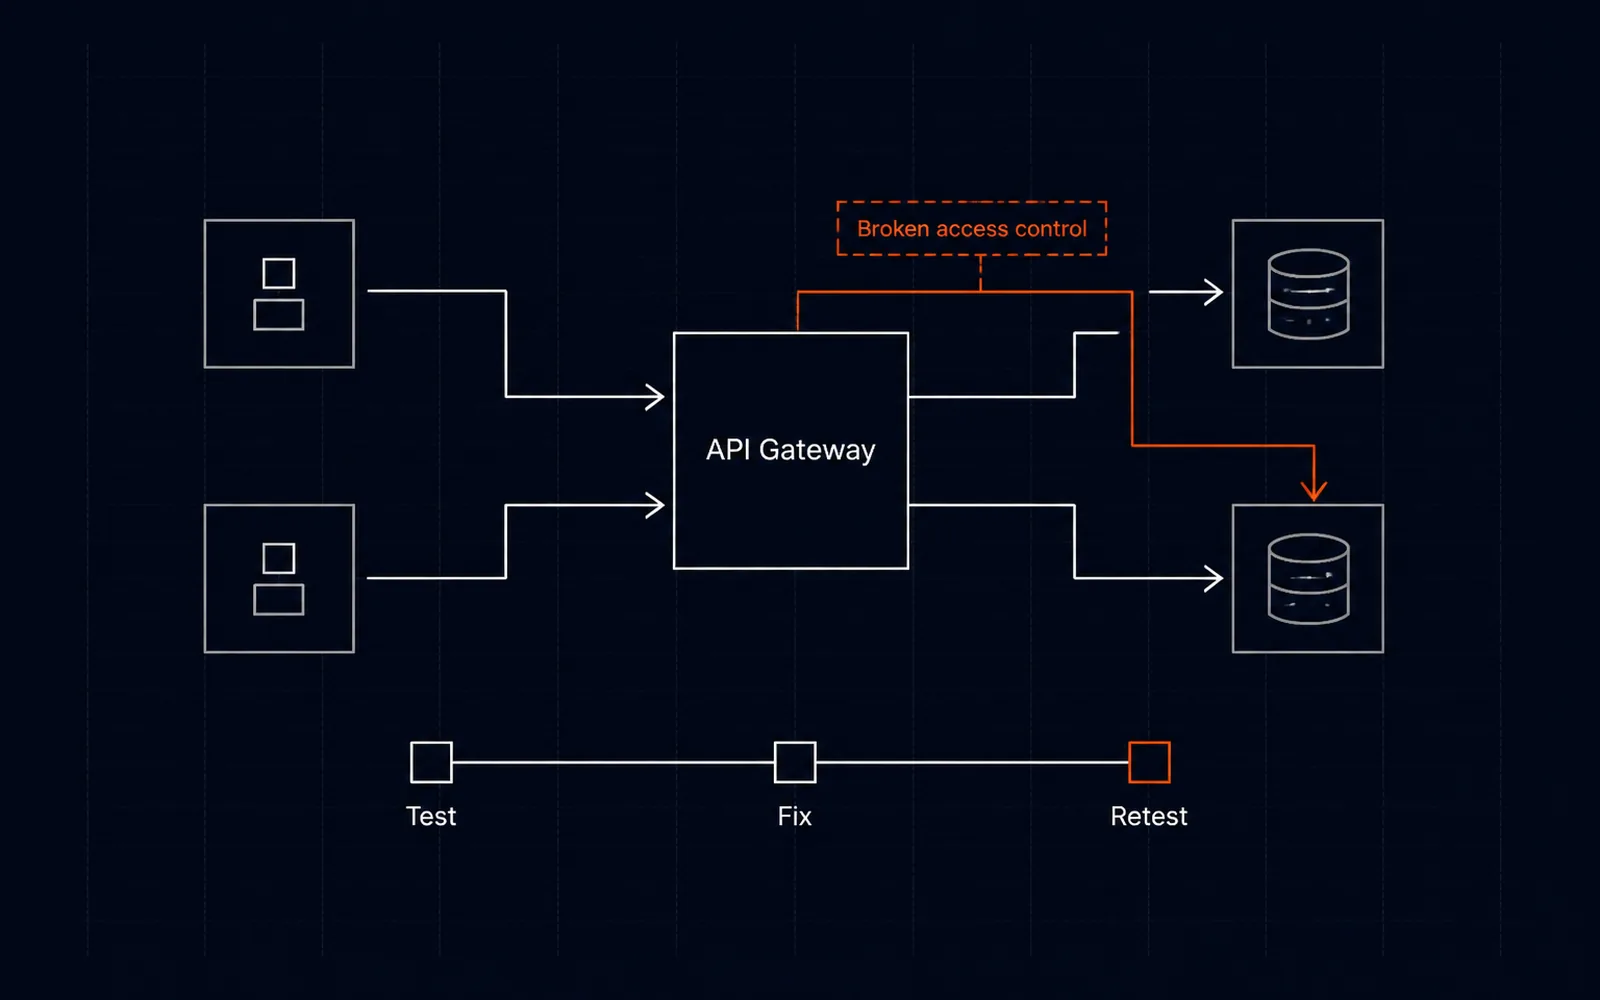
Diagram of a banking API gateway where a cross-account access flaw was found, fixed and retested

VAPT · Fintech & Banking

Closing Critical Gaps in a Banking API Gateway

A regional bank needed a full penetration test of its customer-facing API gateway ahead of launch. We found 9 issues, including a critical broken access control flaw, and retested every fix before a 3-week deadline.

FAQ

Frequently Asked Questions About VAPT Services

What is VAPT?

VAPT stands for Vulnerability Assessment and Penetration Testing. It combines vulnerability scanning with manual security testing to identify, validate and prioritize security weaknesses across applications, APIs, networks and IT infrastructure.

What does a VAPT service provider do?

A VAPT service provider assesses your digital assets for security vulnerabilities and validates exploitable weaknesses through controlled penetration testing. At CipherTrivia, we provide technical findings with severity ratings, evidence and remediation recommendations.

Why is VAPT testing important for businesses?

VAPT testing helps businesses identify security vulnerabilities before attackers can exploit them. It can reduce security risks across web applications, mobile applications, APIs and infrastructure while supporting internal security assessments and compliance requirements.

What types of VAPT services does CipherTrivia provide?

We provide web application VAPT, mobile application VAPT, API penetration testing, network VAPT and infrastructure security testing. Our assessments can be scoped according to the applications and infrastructure being tested.

How does CipherTrivia perform VAPT testing?

We follow a structured process that covers scope definition, vulnerability assessment, manual penetration testing, vulnerability validation, risk classification, reporting and retesting. Our approach combines automated security tools with manual testing performed by security professionals.

Does VAPT include manual penetration testing?

Yes. Our VAPT security services include manual validation and penetration testing to investigate vulnerabilities identified through automated assessment. Manual testing also helps uncover security issues that automated scanners may not detect.

Do you provide a VAPT report?

Yes. We provide a detailed VAPT security assessment report containing vulnerability descriptions, severity ratings, technical evidence, affected assets and remediation recommendations. Reports can also include relevant OWASP, CWE and CVSS references.

What vulnerabilities can VAPT identify?

VAPT can identify vulnerabilities such as SQL injection, Cross-Site Scripting (XSS), broken access control, authentication weaknesses, privilege escalation, insecure configurations, sensitive data exposure and API security vulnerabilities.

Does CipherTrivia provide VAPT retesting?

Yes. After vulnerabilities are remediated, we can perform VAPT retesting to verify the implemented fixes. The retest results can be documented in a closure report for internal security teams and relevant stakeholders.

How long does a VAPT assessment take?

The duration depends on the scope and complexity of the environment being tested. Factors such as the number of applications, APIs, IP addresses, user roles and testing requirements can affect the overall VAPT assessment timeline.

Can VAPT support compliance and security audits?

Yes. A properly documented VAPT assessment can support security and audit activities by providing evidence of vulnerability testing and remediation. Our reports can include industry references such as OWASP, CWE and CVSS based on the assessment scope.

Does CipherTrivia use AI in VAPT security testing?

We use AI-assisted security analysis to support activities such as vulnerability analysis and technical review. Human security expertise remains central to our VAPT methodology, with findings requiring appropriate validation before inclusion in the final report.

Get Started With Our VAPT Security Services

Tell us about your application, API, cloud or network environment and we'll scope a VAPT security services engagement that fits your timeline and budget.

Quick inquiry

Get a quote for VAPT Security Services

We'll review your current setup, map the right testing approach, and outline timelines and pricing, with no obligation.

  • Reply within one business day, Monday–Friday IST
  • Your NDA or ours, signed before any scoping discussion
  • A free retest after your fixes

Call +91 90083 72466 WhatsApp projects@ciphertrivia.com

Tell us about your use case