Experiencing a security incident? Get emergency responseCall now +91 90083 72466 Quick inquiry

Penetration Testing Services to Identify Security Vulnerabilities

CipherTrivia delivers professional penetration testing services to identify exploitable vulnerabilities across web applications, mobile apps, APIs, networks and cloud infrastructure. Our security testing approach simulates real-world attack scenarios to evaluate security weaknesses, assess potential business risks and provide actionable remediation recommendations that strengthen your organization's security posture.

Code on a monitor in a dimly lit security testing workstation
Reporting mapped to OWASP Top 10 OWASP API Top 10 CWE CVSS ISO 27001 SOC 2 PCI DSS

Identify Security Weaknesses with Expert Penetration Testing

CipherTrivia delivers comprehensive penetration testing services to help organizations identify exploitable vulnerabilities and understand how attackers could compromise their digital assets. Penetration testing services involve testing websites, applications, APIs, networks and cloud environments to identify security vulnerabilities that attackers could exploit. The assessment helps businesses understand potential risks and take corrective action to protect sensitive data and critical systems.

Our testing evaluates web applications, mobile applications, APIs, networks and cloud environments to uncover security gaps that may expose sensitive data or disrupt business operations.

Our penetration testing approach combines manual security analysis with specialized testing tools to examine authentication mechanisms, access controls, application logic, network configurations and potential attack paths. Findings are validated within the agreed testing scope and prioritized according to severity and business impact.

As a provider of penetration testing services, CipherTrivia delivers detailed technical reports with evidence-based findings and practical remediation guidance. These insights help development and IT teams address vulnerabilities, strengthen security controls and improve resilience against evolving cyber threats.

Our services support organizations seeking to assess their security posture, validate existing protections and reduce exposure to attacks through structured, risk-based security testing.
Types of Penetration Testing Services We Provide

CipherTrivia offers penetration testing services to help organizations identify exploitable security weaknesses across applications, APIs, networks and cloud infrastructure. Our assessments simulate realistic attack scenarios within an authorized scope to evaluate security controls, validate vulnerabilities and provide practical remediation recommendations.

Web Application Penetration Testing

We assess web applications for vulnerabilities involving authentication, session management, access controls, input validation and business logic. Testing helps identify weaknesses that could expose sensitive information or allow unauthorized actions.

Mobile Application Penetration Testing

We evaluate Android and iOS applications for insecure data storage, weak authentication, improper permissions, insecure API communication and other mobile-specific security risks.

API Penetration Testing

Our API testing examines authentication, authorization, object-level access controls, rate limiting and data exposure. It helps identify weaknesses in REST and GraphQL APIs that could allow unauthorized access or misuse of business functionality.

Network Penetration Testing

We assess internal and external networks for exposed services, insecure configurations, weak access controls and exploitable vulnerabilities. Testing helps organizations understand potential attack paths across their network infrastructure.

Cloud Penetration Testing

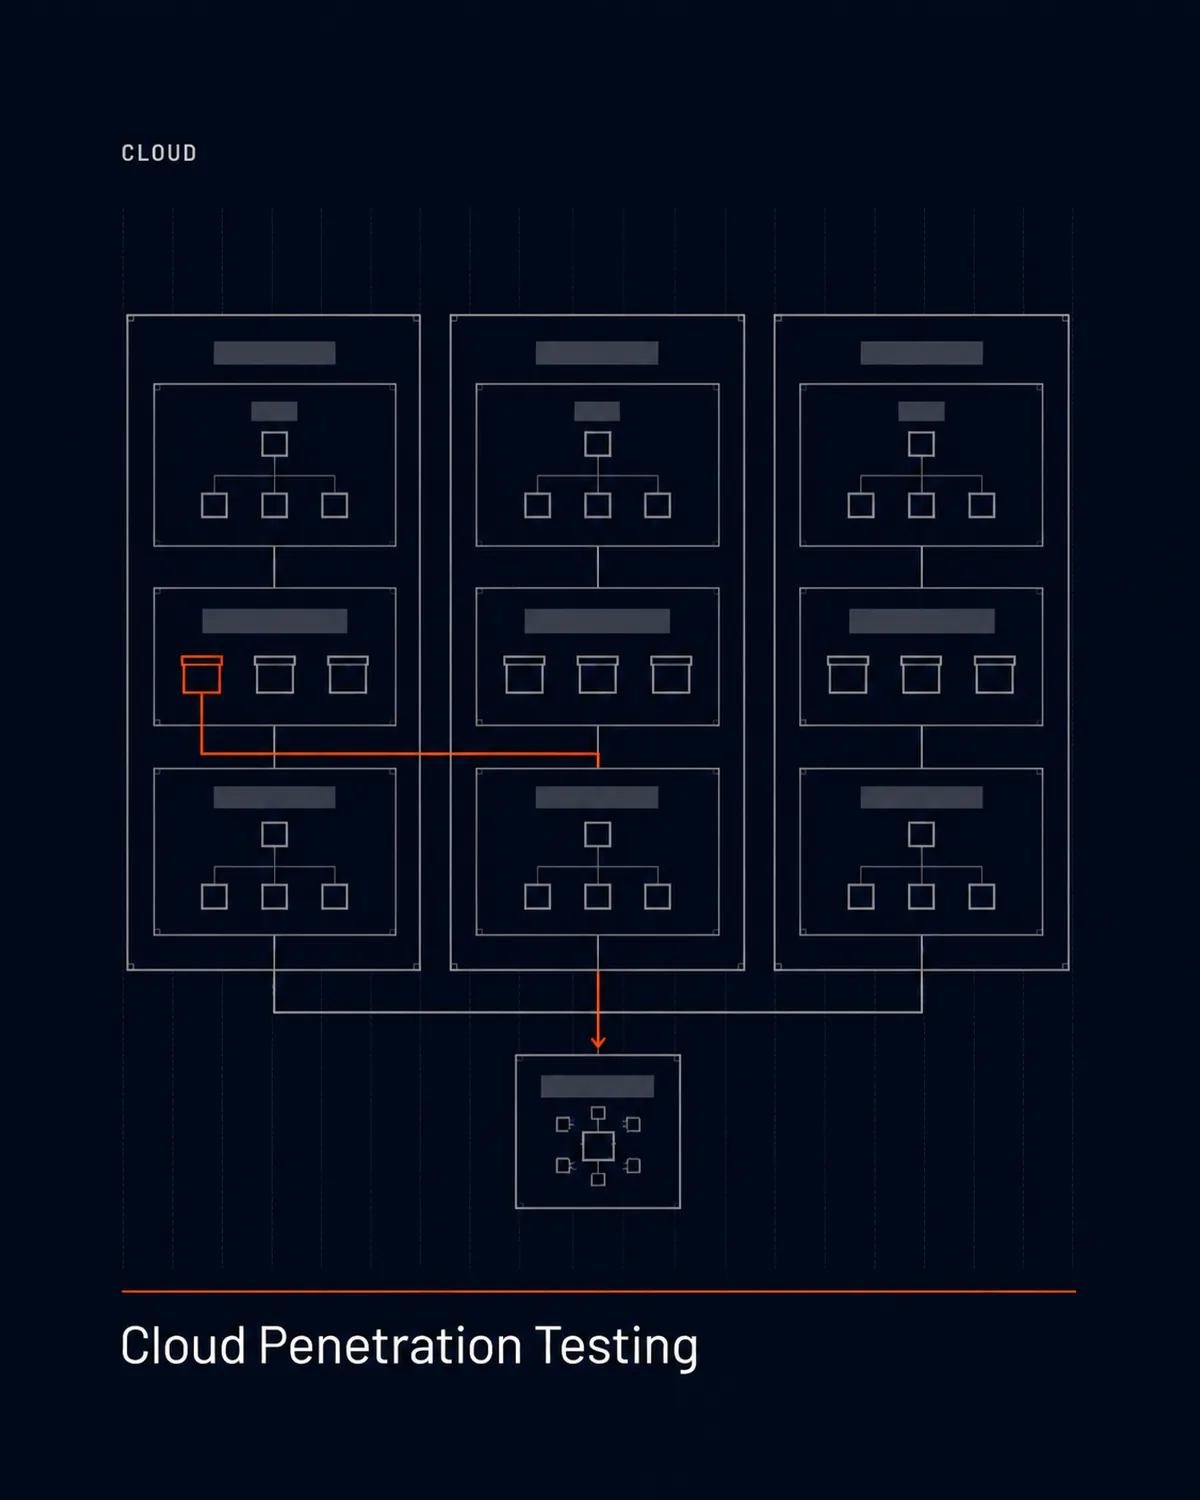
We assess in-scope cloud environments hosted on AWS, Microsoft Azure or Google Cloud for exploitable configuration weaknesses, excessive permissions, exposed services and potential paths to unauthorized resource access.

Wireless Network Penetration Testing

We evaluate authorized wireless networks for weak encryption, insecure configurations, authentication weaknesses and potential unauthorized access to identify risks affecting wireless connectivity.

Red Team Assessment

We simulate defined attacker objectives to evaluate how effectively security controls detect and respond to realistic attack techniques. Depending on the engagement scope, testing may cover technology, detection capabilities and incident response processes.

Active Directory & Internal Security Testing

We examine identity infrastructure, privilege assignments, authentication policies and internal attack paths to identify weaknesses that could allow an attacker to escalate privileges or move across systems.

What Our Penetration Testing Services Cover

Our penetration testing services help businesses identify exploitable vulnerabilities across applications, APIs, mobile platforms, cloud environments and internal networks. CipherTrivia simulates real-world attack scenarios within an authorized testing scope to assess security controls, uncover potential attack paths and recommend corrective actions based on risk severity and business impact.

Web Application Penetration Testing

We test web applications for authentication bypass, session hijacking, SQL injection, cross-site scripting (XSS), server-side request forgery (SSRF) and insecure access controls. Assessments reference relevant OWASP Top 10 risks and applicable application security testing standards.

API Penetration Testing (REST & GraphQL)

Our API penetration testing services evaluate authentication and authorization controls, broken object-level authorization (BOLA), excessive data exposure, injection vulnerabilities and rate-limit weaknesses. Testing helps identify API security gaps that could expose sensitive data or permit unauthorized operations.

Mobile Application Penetration Testing

We assess Android and iOS applications for insecure data storage, weak authentication, certificate validation weaknesses, runtime vulnerabilities and insecure API communication. Testing follows relevant OWASP Mobile Application Security guidance to identify risks affecting mobile users and backend systems.

Cloud Penetration Testing

Our cloud penetration testing services assess authorized AWS, Microsoft Azure and Google Cloud Platform (GCP) environments for excessive permissions, exposed resources, insecure storage, identity and access management weaknesses and configuration flaws. The assessment identifies potential attack paths that could compromise cloud workloads or sensitive information.

Internal Network & Active Directory Penetration Testing

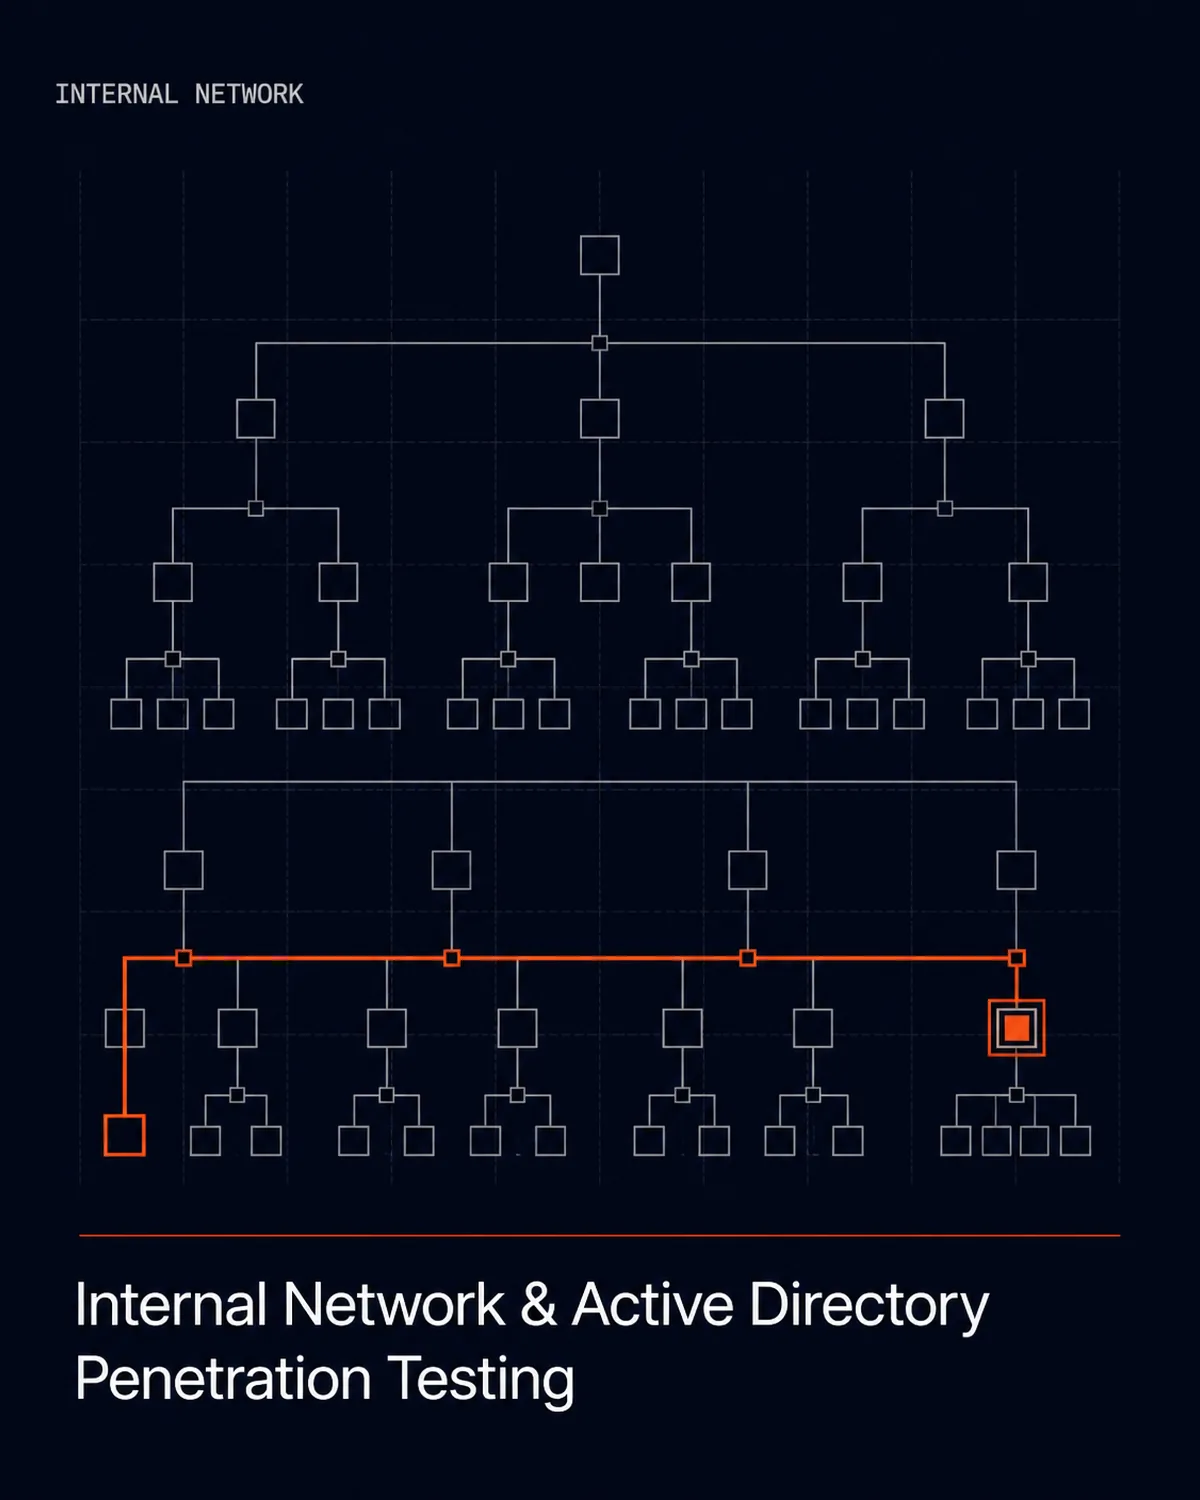
We evaluate internal network security and Active Directory environments for privilege escalation, weak authentication policies, credential exposure, Kerberos-related weaknesses and lateral movement opportunities. These assessments help organizations understand how an attacker with initial network access could compromise additional systems.

Wireless & Physical Security Testing

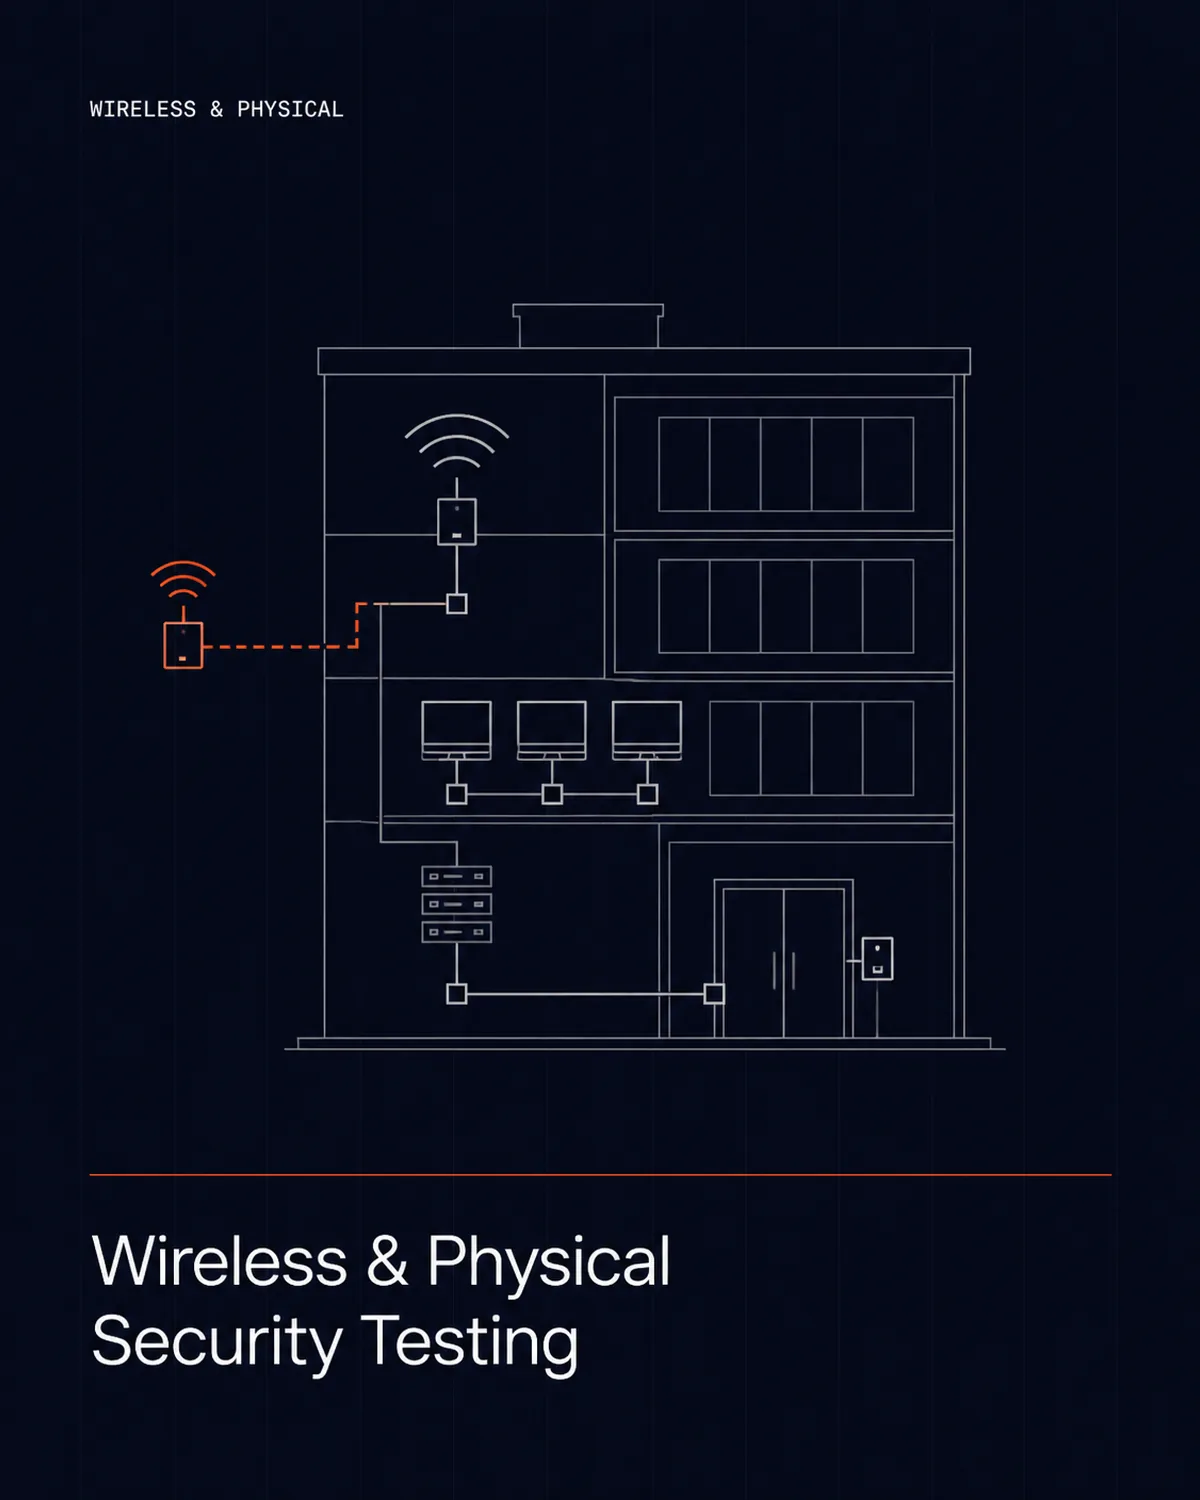
We assess authorized wireless networks for weak encryption, insecure configurations, rogue access points and authentication weaknesses. Where explicitly included in scope, physical security testing can evaluate access controls, badge procedures and other potential entry points into protected facilities.

Identify Risks. Prioritize Remediation. Strengthen Security.

CipherTrivia delivers penetration testing services with validated findings, risk-based severity ratings and practical remediation guidance. Our reports help security and development teams address exploitable weaknesses while supporting stronger application security, cloud protection and network resilience.

Attack Scenarios Our Penetration Testing Services Simulate

CipherTrivia's penetration testing services simulate realistic cyberattacks within an authorized testing scope to identify exploitable weaknesses and evaluate how existing security controls respond to threats. These assessments help organizations understand potential attack paths, measure security gaps and prioritize remediation before vulnerabilities are exploited by malicious actors.

Unauthorized Access & Authentication Bypass

We test authentication mechanisms, session management and access controls to identify weaknesses that could allow attackers to bypass login protections, hijack sessions or access restricted resources.

Privilege Escalation

Our testing examines whether weaknesses in user permissions, system configurations or identity controls could allow a low-privileged user to gain unauthorized administrative access to critical systems.

Sensitive Data Exposure

We assess applications, APIs, databases and cloud storage for vulnerabilities that could expose confidential business information, customer records, credentials or personal data to unauthorized users.

Injection Attacks & Remote Code Execution

We test for vulnerabilities such as SQL injection, command injection and cross-site scripting (XSS) to determine whether untrusted input could compromise application functionality, expose data or allow unauthorized actions.

Lateral Movement & Internal Network Compromise

We simulate attack paths within authorized internal environments to identify how compromised credentials or vulnerable systems could allow attackers to move between devices, access additional resources or reach critical infrastructure.

Cloud Misconfiguration Exploitation

We evaluate cloud environments for excessive permissions, exposed storage, insecure identity policies and misconfigured services that could create opportunities for unauthorized access or compromise of cloud resources.

API Abuse & Business Logic Exploitation

We examine APIs and application workflows for broken access controls, parameter manipulation, excessive data exposure and business logic flaws that could allow unauthorized transactions or misuse of application functionality.

Security Control & Detection Gaps

We evaluate how existing security controls respond to approved attack simulations and identify gaps in logging, monitoring, alerting and incident response that may delay threat detection.

Strengthen Defences Through Realistic Attack Simulation

Our penetration testing services provide evidence-based findings, risk severity ratings and actionable remediation recommendations. This helps security teams understand how vulnerabilities could affect business operations and prioritize improvements across applications, APIs, networks and cloud infrastructure.

Our Penetration Testing Process

Our penetration testing process helps businesses identify security weaknesses, understand potential risks and take the right steps to protect their digital assets. CipherTrivia follows a structured approach to assess your systems, explain the findings in simple terms and recommend practical improvements.

  1. Understanding Your Requirements

    We understand your business needs and identify the websites, applications, networks or cloud systems that need testing. Our team defines the testing scope and objectives before the assessment begins.

  2. Identifying Potential Weaknesses

    We examine your systems to identify security gaps, weak access controls and potential entry points that attackers could exploit. This helps us understand where your digital assets may be at risk.

  3. Testing Security Risks

    We safely test identified weaknesses to understand how they could affect your systems and business operations. This helps determine which issues could lead to unauthorized access, data exposure or service disruption.

  4. Evaluating Risk & Impact

    We prioritize the identified issues based on their seriousness and potential impact on your business. This helps your team focus first on the most critical security risks.

  5. Sharing Findings & Recommendations

    We provide a clear penetration testing report explaining the identified weaknesses, their potential impact and the recommended steps to fix them. The report helps technical teams and business stakeholders understand what needs attention.

  6. Retesting & Verification

    After the recommended fixes are implemented, we can retest the affected systems, where included in the agreed scope, to check whether the identified issues have been resolved.

What You Receive From Our Penetration Testing Services

Our penetration testing services provide clear reports and practical recommendations to help businesses understand security vulnerabilities and take corrective action. CipherTrivia delivers actionable findings for technical teams while giving management the insights needed to assess security risks, prioritize fixes and strengthen protection against cyberattacks.

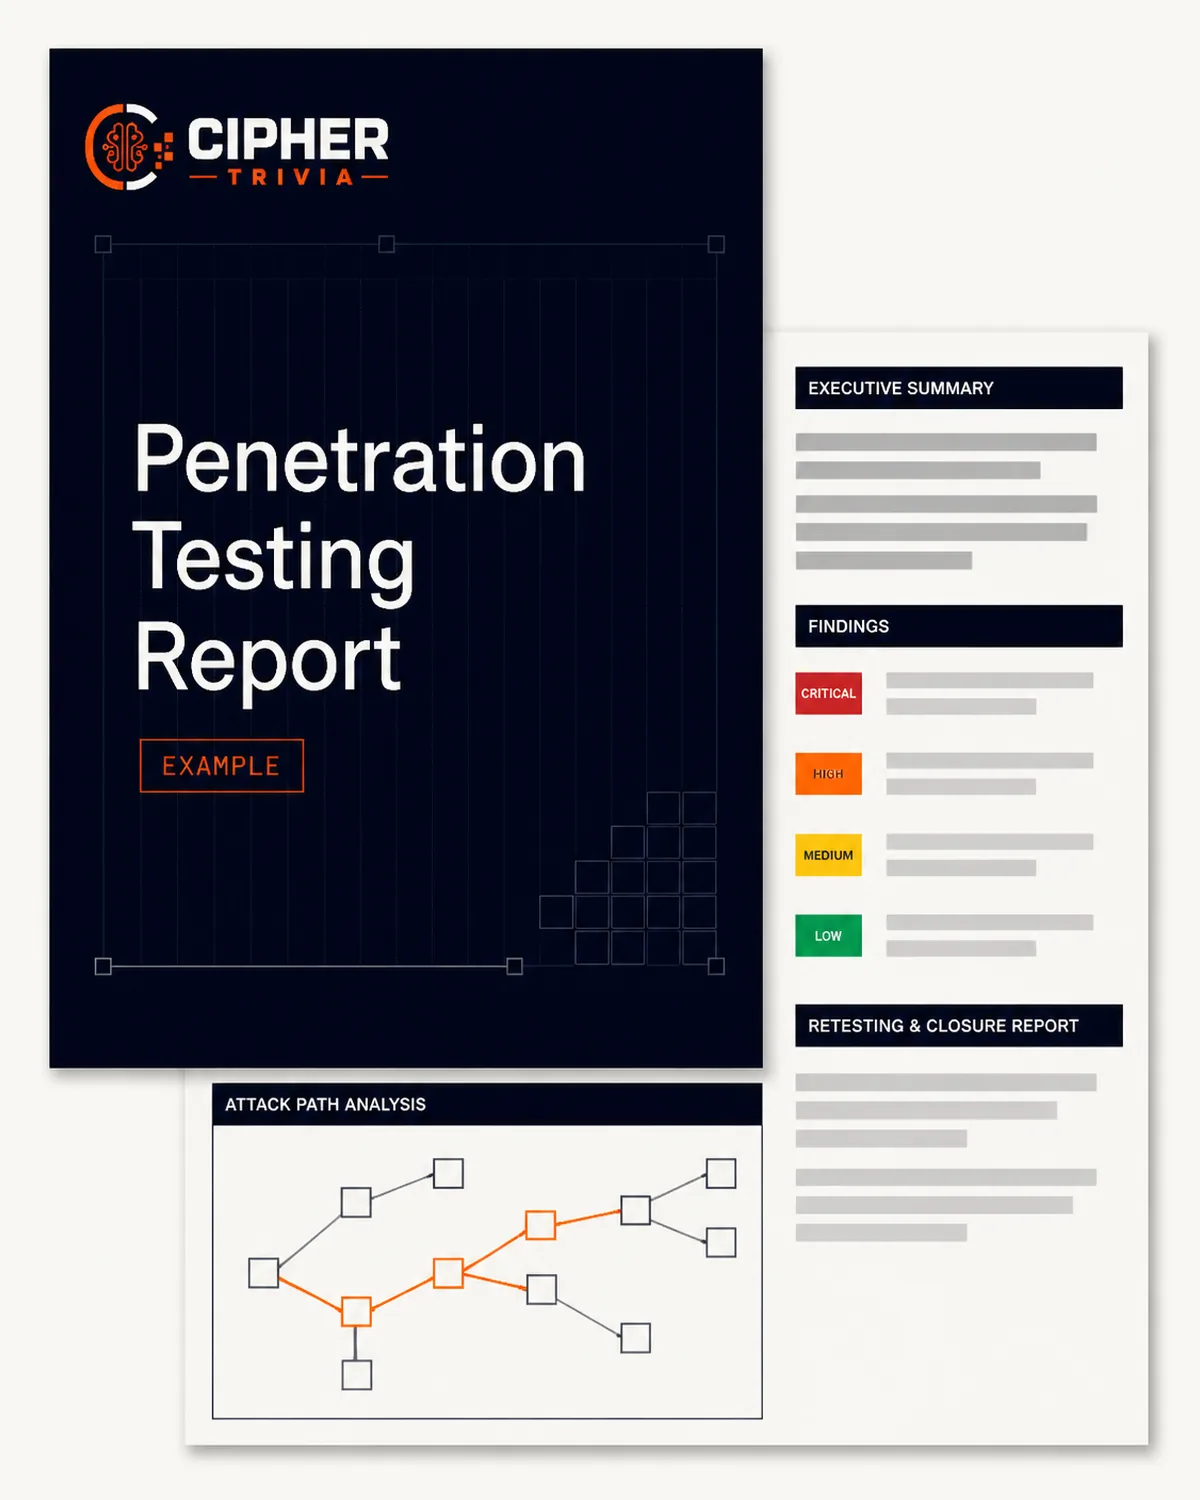
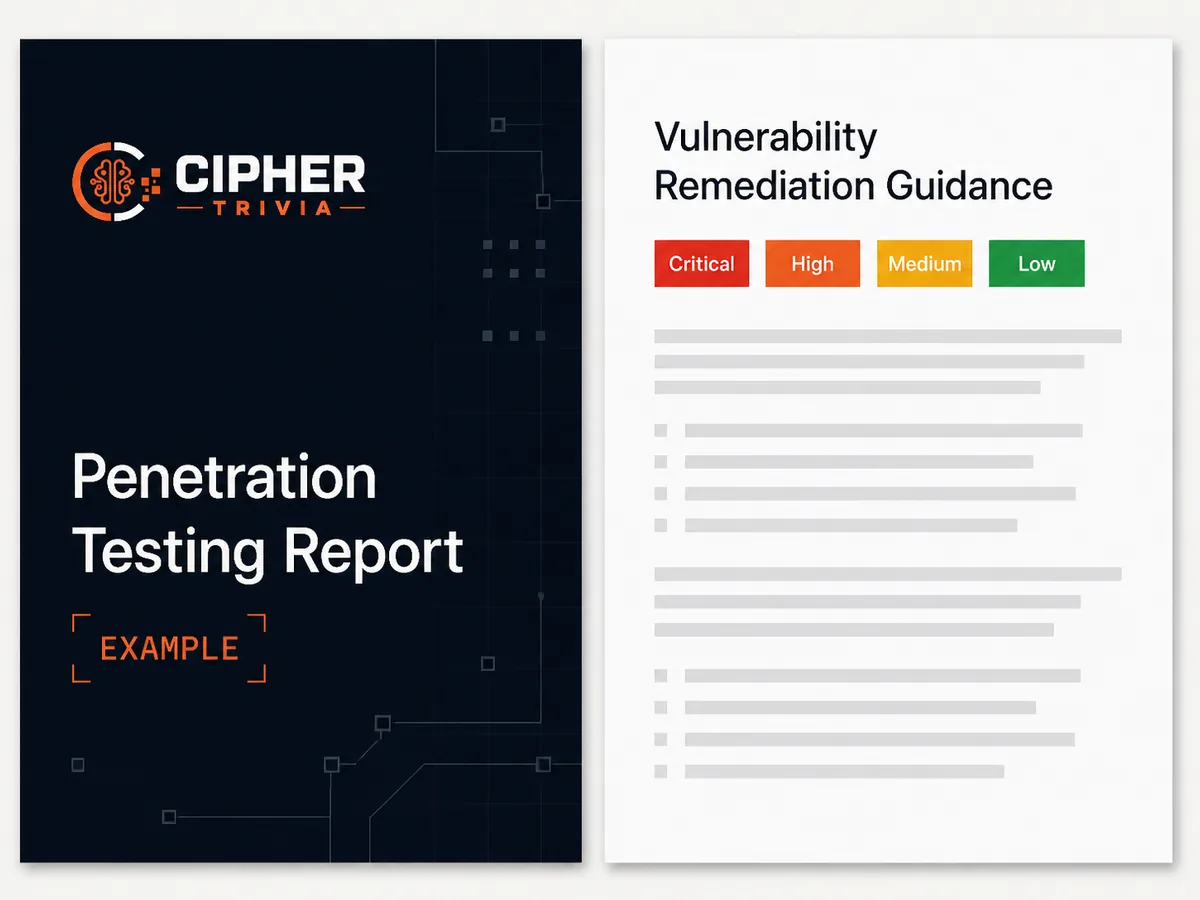
Example penetration testing report with an attack path analysis and rated findings
  1. Executive Summary

    A clear overview of your security assessment highlighting the most important security risks, critical vulnerabilities and potential business impact. It helps management understand the current security posture and prioritize improvements without requiring deep technical knowledge.

  2. Penetration Testing Report

    A detailed report documenting identified and verified security vulnerabilities, their severity, supporting evidence and potential impact. The findings help technical teams understand where weaknesses exist and how they could affect applications, networks or business data.

  3. Attack Path Analysis

    A visual explanation of how multiple security weaknesses could be connected to create a potential attack path. This helps your team understand how attackers might gain unauthorized access, move between systems or reach sensitive information.

  4. Vulnerability Remediation Guidance

    Practical recommendations for fixing identified vulnerabilities and improving existing security controls. Each finding includes prioritized corrective actions to help development and IT teams address security gaps efficiently.

  5. Retesting & Closure Report

    After fixes are implemented, we can retest identified vulnerabilities as agreed in the engagement scope. The closure report records the remediation status, highlights resolved issues and identifies any remaining findings that require attention.

Sample penetration testing report cover and findings page

Identify Vulnerabilities. Fix Security Gaps. Strengthen Protection.

Get clear penetration testing reports, prioritized remediation guidance and actionable insights to improve your security posture.

Why Choose CipherTrivia for Penetration Testing Services?

CipherTrivia provides penetration testing services that help businesses identify security vulnerabilities, understand potential attack risks and take practical steps to protect their digital assets. Our approach focuses on clear findings, risk-based recommendations and actionable reports that help teams make informed security decisions.

Practical, Risk-Based Testing

We assess your applications, APIs, networks and cloud environments to identify weaknesses that could expose sensitive data or disrupt business operations. Findings are prioritized according to severity and potential business impact.

Manual Testing & Tool-Assisted Analysis

Our testing approach combines manual security checks with specialized testing tools to investigate potential vulnerabilities and validate findings beyond automated scan results.

Clear Reports & Actionable Guidance

We provide detailed penetration testing reports that explain identified vulnerabilities, their potential impact and recommended corrective actions. This helps technical teams understand what needs to be fixed and where to focus first.

Testing Aligned With Industry Standards

Our assessments can reference recognized security guidance such as the OWASP Top 10 and OWASP Web Security Testing Guide, depending on the type of system being tested and the engagement scope.

Coverage Across Multiple Technologies

Our penetration testing services can assess web applications, mobile apps, APIs, internal networks and cloud environments. This helps organizations identify security gaps across different parts of their digital infrastructure.

Retesting & Remediation Verification

Where included in the agreed scope, we retest vulnerabilities after fixes are applied to verify remediation progress and identify issues that may still require attention.

Protect Your Business With Proactive Security Testing

Identify exploitable weaknesses before they become serious security incidents. Connect with CipherTrivia to discuss your penetration testing requirements and determine the right assessment scope for your business.

Frequently Asked Questions About Penetration Testing Services

Penetration testing helps identify security weaknesses before attackers exploit them. It supports risk reduction, data protection and stronger security controls while helping organizations understand how vulnerabilities could affect business operations.

CipherTrivia offers penetration testing across web applications, mobile applications, APIs, internal and external networks, cloud environments and wireless networks, depending on the agreed testing scope and service availability.

Businesses commonly conduct penetration testing annually and after significant changes to applications, infrastructure or security controls. Testing may also be required following major releases, security incidents or compliance reviews.

A vulnerability assessment identifies and evaluates potential security weaknesses. Penetration testing goes further by safely validating selected vulnerabilities to understand how they could be exploited and what impact they may have.

The timeline depends on the number of systems, application complexity, testing scope and environment size. A focused assessment may take a few days, while larger applications or infrastructure environments may require several weeks.

A penetration testing report typically includes identified vulnerabilities, severity ratings, supporting evidence, potential business impact and recommended fixes. Depending on the engagement, it may also include an executive summary, attack path analysis and retesting results.

Penetration testing is planned to minimize disruption through agreed testing boundaries and controlled methods. Some tests can affect system availability, so testing conditions, exclusions and safeguards should be established before work begins.

Yes. Penetration testing can support security and compliance activities associated with standards such as PCI DSS, ISO 27001 and SOC 2, where relevant. Testing alone does not guarantee certification or compliance, but its findings can help address security control gaps.

The testing team documents the findings and provides remediation recommendations based on risk and severity. Your technical team can then implement fixes, followed by retesting where included in the engagement scope to verify whether the issues have been resolved.

Cloud penetration testing examines authorized cloud environments such as AWS, Microsoft Azure and Google Cloud for weaknesses involving access permissions, exposed resources, insecure configurations and potential unauthorized access paths.

Contact CipherTrivia to discuss your applications, infrastructure, security concerns and testing objectives. Based on your requirements, the assessment scope can be defined to identify relevant security risks and provide actionable remediation guidance.

Quick inquiry

Get a quote for Penetration Testing

We'll review your current setup, map the right testing approach, and outline timelines and pricing, with no obligation.

  • Reply within one business day, Monday–Friday IST
  • Your NDA or ours, signed before any scoping discussion
  • A free retest after your fixes

Call +91 90083 72466 WhatsApp projects@ciphertrivia.com

Tell us about your use case